

I am using wp-admin-cleaner version 2.0.1 (latest version as far as I know) and have a plugin that provides a User Adit tool.
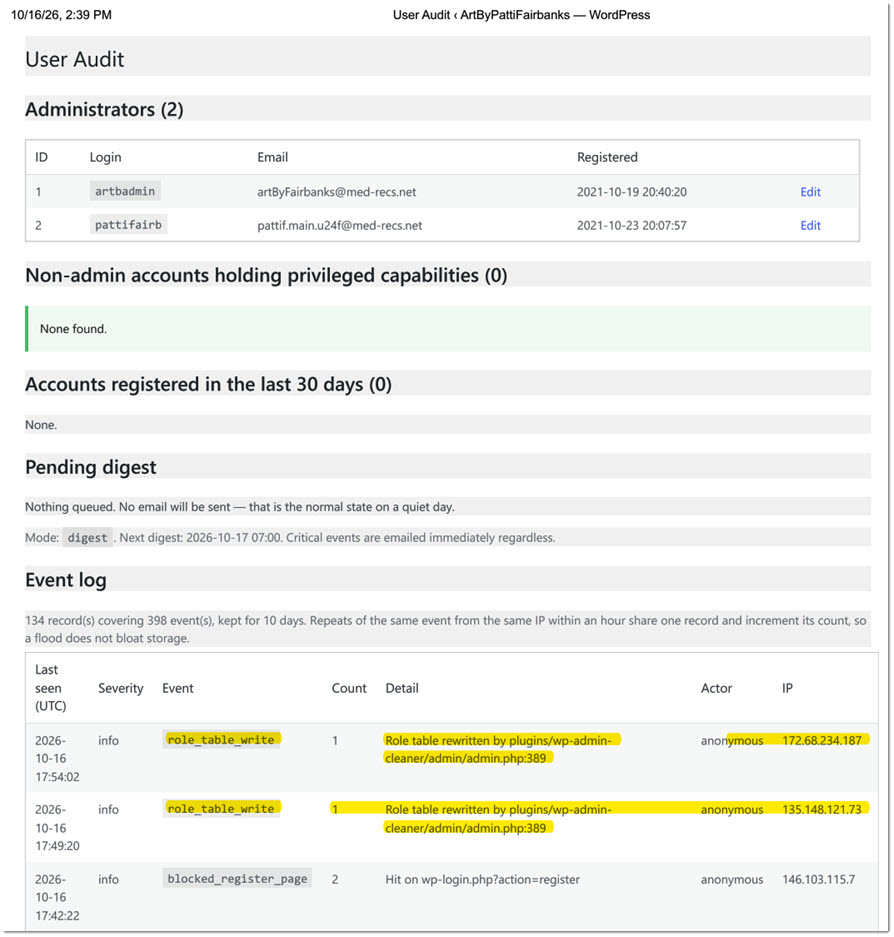
I see many entries containing the following is one example (of hundreds) for hacker behaviour via wp-admin-cleaner:
- Event: role_table_write
- Count: 11 <most reports have 1 or 2 counts>
- Detail: Role table rewritten by plugins/wp-admin-cleaner/admin/admin.php:389
- Actor: anonymous
- IP: 135.148.121.73 <but there are hundreds in the list of Event records>
See the PDF document in the link for more info.
https://www.artbypattifairbanks.com/_downloads/Hacked%20dPlugins%20wp-admin-cleaner%20(User%20Audit)ArtByPattiFairbanks%2026oct16_citi(pw).pdf
The password to open/view the PDF is: surrey
Please reply to acknowledge my support request.
I am concerned about this vulnerability. Please fix ASAP.
Thank you.
Peter
PS: I will provide WP Login info upon your request, if needed.
Uploaded files:
Thanks for the info.
It’s moved to todo.
Will investigate and release hotfix if valid.
best
Marko